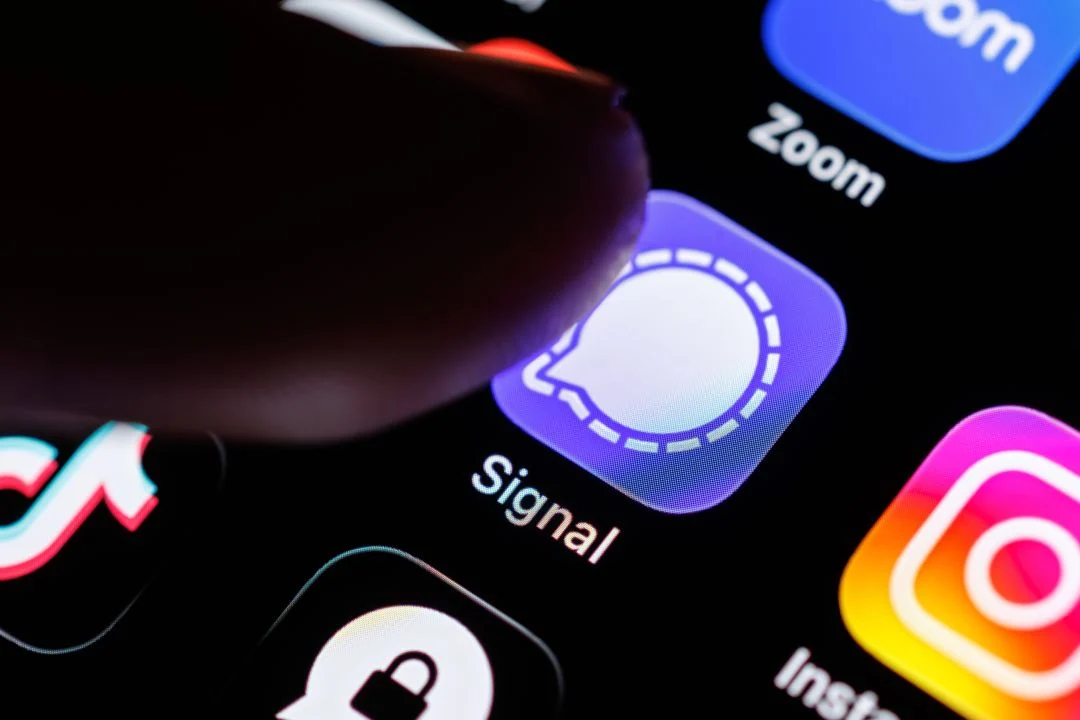
Privacy-focused messaging platform Signal has announced a significant update aimed at restricting users’ ability to take screenshots within its application on mobile operating systems. Disclosed on Friday, November 21, 2026, the update represents a defensive measure against what Signal President Meredith Whittaker has characterized as an "existential threat" posed by modern operating systems deeply integrated with agentic artificial intelligence. This technical shift marks a major escalation in the ongoing tension between private communication developers and major tech ecosystems that embed persistent AI tracking features directly into desktop and mobile environments.
The core of the issue lies in the evolution of operating systems such as Microsoft Windows, Google Android, Apple macOS, and iOS. As these platforms introduce sophisticated agentic AI capabilities—software agents designed to autonomously scan, interpret, and manage data across a user’s device—they fundamentally alter the security landscape. Whittaker explained in a formal company blog post that by giving AI agents continuous, system-level permission to scan and analyze information displayed on users’ screens, these operating systems are actively undermining Signal’s foundational promise: the independent guarantee of end-to-end encrypted privacy.
According to Signal’s leadership, once an OS-level AI agent captures sensitive text, media, or metadata displayed within an application, that information is frequently logged, stored, and routed to local databases or remote cloud servers dictated by the operating system manufacturer. Because this capture mechanism operates outside the boundary of Signal’s end-to-end encryption architecture, the messaging platform loses all administrative and technical control over the data. This leakage not only exposes individual users to third-party data harvesting but also imperils the privacy of every participant involved in a secure conversation.
Background Context and Evolution of the Threat Model
For years, the primary threat vector to secure messaging applications involved traditional malware, device theft, or physical observation over a user’s shoulder. To mitigate these risks, secure messaging developers implemented various hardening techniques, including secure view flags, app-switching previews redaction, and optional screenshot blocking. Signal had previously deployed measures to block screenshots by default within its desktop application for Windows, recognizing the historical vulnerability of desktop operating systems to background scraping and telemetry collection.
However, the rapid acceleration of generative AI and autonomous software agents throughout 2024, 2025, and into 2026 has radically transformed the operating system market. Features like Microsoft’s controversial Recall tool, alongside equivalent ambient intelligence features integrated natively into modern mobile operating systems, continuously record and index everything a user sees and does on their device. These tools are designed to provide seamless cross-application searchability and automated task execution. From a privacy engineering perspective, however, these agentic systems function as sophisticated, highly authorized spyware built directly into the foundational software layer of the consumer device.
Signal’s leadership realized that traditional end-to-end encryption—which protects data while it is in transit across networks—is rendered functionally obsolete if the endpoints (the user’s physical screens) are continuously monitored by automated AI systems that exfiltrate data to external servers. Consequently, the decision to restrict in-app screenshots across Android and iOS is a necessary, albeit reactive, attempt to build a perimeter defense against system-level intrusion.
Technical Implementation and User Experience Impact
The newly implemented restrictions modify how Signal interacts with the native display compositor of Android and iOS devices. By default, the application will now enforce strict anti-screenshot and anti-screen-recording protocols, aligning mobile behavior with the existing desktop posture.

Despite the strict security default, Signal has retained a degree of user flexibility by allowing individuals to manually disable the restriction within the application’s settings menu. However, this flexibility comes with a stark warning from platform executives. Whittaker openly acknowledged that toggling off the protection effectively "breaks our privacy guarantees." Furthermore, Whittaker candidly admitted that this software update is an "incomplete" solution. While it successfully blocks standard, explicit screenshot captures, it cannot comprehensively address more sophisticated or stealthy methods that advanced AI agents might employ to read application data via background APIs, accessibility services, or auxiliary memory inspection.
Industry Reactions and the Broader Privacy Debate
The announcement has triggered intense discussions across the cybersecurity, software development, and digital civil liberties communities. Independent security researchers have largely validated Signal’s concerns, noting that the architectural design of modern agentic AI operating systems is fundamentally incompatible with strict data minimization and confidentiality standards.
Conversely, major technology conglomerates developing these operating systems have defended agentic AI integration as a revolutionary productivity leap designed with robust user consent mechanisms and local data processing safeguards. Representatives from major mobile OS ecosystems argue that users maintain granular control over which applications are monitored by AI agents and that enterprise-grade security controls allow organizations to disable such features entirely in regulated environments.
However, privacy advocates argue that consent models involving complex, multi-layered operating system settings are often opaque to the average consumer, resulting in unwitting compliance with continuous surveillance practices. Signal’s preemptive move highlights a growing institutional divide: while platform vendors are racing to embed cloud-connected and locally cached AI agents into every corner of the digital experience, independent communication tools are forced to build operational walls to protect basic user confidentiality.
Implications for the Future of Secure Communications
The decision by Signal to restrict mobile screenshots underscores a troubling reality for the future of secure messaging. As operating systems become more intelligent, autonomous, and intrusive, the traditional boundaries separating the application layer from the operating system layer are blurring. Application developers can no longer assume that the underlying operating system acts as a neutral, secure host for encrypted communications.
Looking ahead, industry analysts predict a prolonged architectural struggle between operating system vendors and privacy-focused application developers. If OS-level AI agents continue to demand unrestricted access to screen contents and user workflows, niche privacy apps may be forced to explore radical technical departures—such as rendering interfaces through custom, sandboxed display engines or migrating entirely to alternative hardware and software ecosystems designed from the ground up for zero-trust computing.
For now, Signal’s latest restriction serves as a vital defensive stopgap and a high-profile warning to the public. It forces users to confront a fundamental technological trade-off: the convenience of ambient, AI-driven digital assistance versus the fundamental right to private, unmonitored human communication.